Yamong Platform · AI Identity
Set permissions that fit the work assigned to AI.
Connect enterprise IdP information and apply permission ceilings and prohibitions to define each agent’s tool scope.
CAPABILITIES
Start with the employee and business purpose to configure what AI may do.
Employee and organization link
- Input
- Employee and organization data from the enterprise IdP
- Review
- Confirm the agent owner and business responsibility
- Result
- An agent linked to employee context
LLM role proposal
- Input
- Assigned work and LLM-proposed tools and paths
- Review
- Prepare proposed items for comparison with the employee’s IdP permissions
- Result
- A role proposal awaiting review
Compare ceiling, then register
- Input
- Employee maximum permissions and organization prohibitions
- Review
- Check for items above the ceiling or prohibited, then register only the allowed scope
- Result
- A role baseline within the allowed ceiling
Usage-history adjustment
- Input
- Agent usage history and current role
- Review
- Review the basis for adjustments and record baseline changes
- Result
- A policy adjustment with review history
SCENARIOS
Follow the decision from request to next step.
Illustrative workflows based on the console examples.
Scenario 01
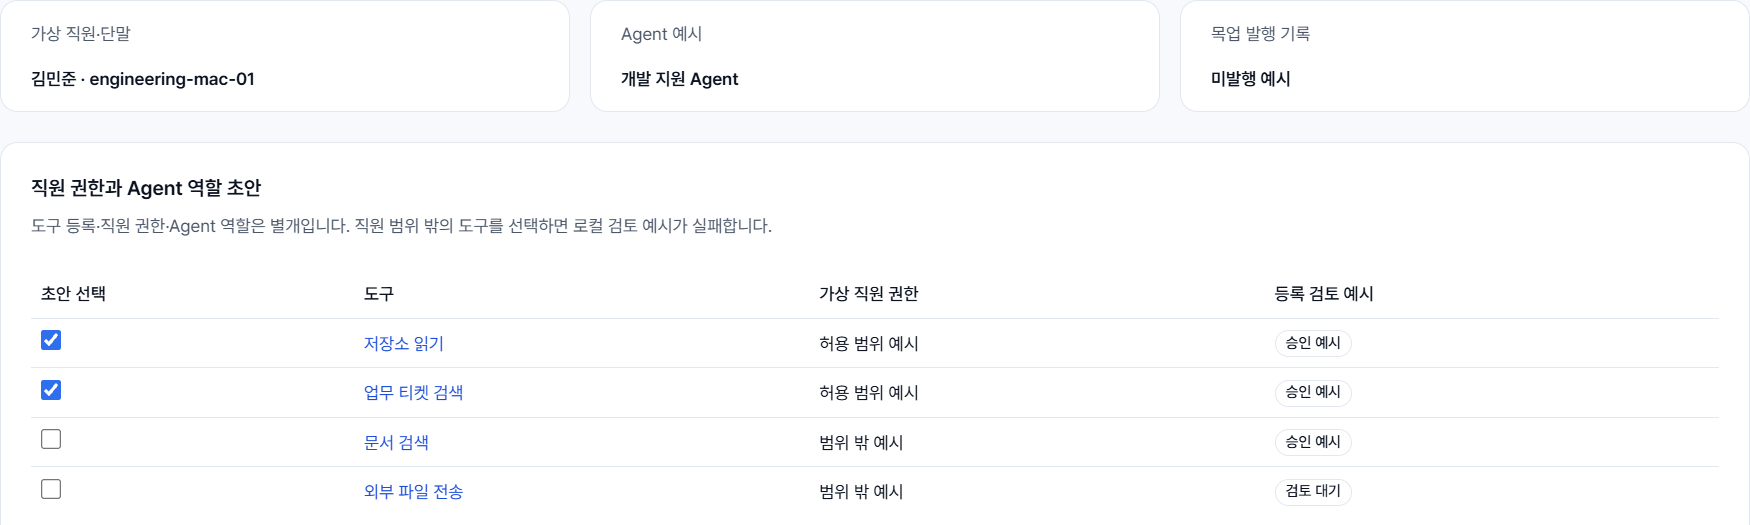
Register an initial development-support role
Minjun Kim’s development-support agent needs repository and work-ticket access.
- Input
- IdP employee/organization data and LLM proposals: repository read, ticket search, document search, external transfer
- Product decision
- The LLM first proposes tools for the business purpose. Then compare with the employee ceiling and prohibitions; register repository read and ticket search only.
- Output / next step
- A role baseline within the allowed scope, with excluded proposals recorded for review
Scenario 02
Revisit a baseline using usage history
A team periodically reviews the usage history of a registered agent.
- Input
- Current role baseline and accumulated usage history
- Product decision
- Review a proposed adjustment against the employee’s maximum permissions and prohibited items again.
- Output / next step
- A reviewable adjustment and change history; each business system still authorizes access to its assets
Illustrative workflows. Actual access is subject to the connected business system’s authentication and authorization.
INTEGRATIONS AND SCOPE
Review the scope for your environment.
Identity applies enterprise IdP permission ceilings and prohibitions to agent role configuration. The connected business system still authorizes access to its own assets; usage-based adjustments provide evidence for policy review.